Showing posts with label hacker. Show all posts

Hostgator docs exposed by S0lar


sOlar from digital-corruption.org have exposed many essential information of the website Hostgator, The biggest web hosting company. He have exposed lots of information including the dox of the owner and some employees. Nameservers , Sql dumps and some emails.


  1.  DoX of the main owner at hostgator
  2. Name: Brent C. Oxley
  3. Age: 29
  4. Lives in: Houston, TX, US
  5. FaceBook: http://www.facebook.com/brentoxley
  6. Twitter: https://twitter.com/#!/hostgator
  7. Myspace: http://www.myspace.com/hostgator
  8. Married to Jessica Michelle Oxley
  9. Wifes facebook: http://www.facebook.com/Jessica.Michelle.Oxley
  10. College he attended: Florida Atlantic University
  11. Image of him: http://blog.hostgator.com/wp-images/biggestloser/brent-oxley_after.jpg

You can find the rest details at the pastebin release
http://pastebin.com/bkqXZpAu

Application Security and Bug Free Coding - The Infographic

Secure Coding and Software Security
Infographic by Veracode Application Security

Sony Pictures Facebook Page and Website Hacked by Anonymous

Hackivist group Anonymous confirmed that they have once again hacked Sony Pictures, gaining access to their Facebook account and website.Anonymous did threaten Sony for supporting the controversial SOPA bill and now it seems that the threats appear real.

The hack sets a spree at Sony Pictures Facebook page and its web site homepage, according to reports and tweets from those involved.


The attacks carry the name Op Sony and were noted through the @s3rver_exe Twitter account.


Anonymous caused a disaster for Sony in 2011 after hacking into the firm's online gaming network and revealing the login information of thousands of users and forcing the system offline for weeks

Hackers Attack City Water Station and Destroys a Pump


Hackers Attack City Water Station and Destroys a Pump
Hackers gained remote access into the control system of the city water utility in Springfield, Illinois, and destroyed a pump last week, according to a report released by a state fusion center and obtained by a security expert.The hackers were discovered on Nov. 8 when a water district employee noticed problems in the city’s Supervisory Control and Data Acquisition System (SCADA). The system kept turning on and off, resulting in the burnout of a water pump.
The intruders launched their attack from IP addresses based in Russia and gained access by first hacking into the network of a software vendor that makes the SCADA system used by the utility. The hackers stole usernames and passwords that the vendor maintained for its customers, and then used those credentials to gain remote access to the utility’s network.
“It is unknown, at this time, the number of SCADA usernames and passwords acquired from the software company’s database and if any additional SCADA systems have been attacked as a result of this theft,” the report states, according to Joe Weiss.

TeaMp0isoN Hacks International Foreign Government E-Mails

Team Poison strikes again
Hex000101 a member of TeaMp0isoN team have hacked and leaked the login credentials of various Government sites after hacking their databases such as armynet.mod.uk and  aph.gov.au .They have released these logins in a pastebin post .This Pastebin post doesn't contain any details or explanations on why the operation took place, but most likely the credentials were leaked as a form of retaliation 
against state institutions. .


Exploiting "Facebook Trusted Friend" Security Feature

Last week Facebook announced that in one day 600,000 accounts possibly get hacked. Another possible solution for Facebook to combat security issues is to find 3 to 5 "Trusted friends". Facebook will be adding two new security features that will allow users to regain control of their account if it gets hijacked.

In Facebook's case, the keys are codes, and the user can choose from three to five "Trusted friends" who are then provided with a code. If you ever get locked out of your account (and you can't access your email to follow the link after resetting your Facebook password), you gather all the codes and use them to gain access to it again.  This method is used by hackers to hack most of the Facebook account using little bit of Social Engineering.


How to hack using this feature ? 


For this technique you need to create 3 fake Facebook account and you need to surely add these as friends into your victims account whose account you are going to hack.
After success full addition of your fake accounts into victims account as friends follow the below steps .:


1. Go to Facebook and click Forgot your Password ?


2. Than you will get something like below just enter the details you know about him enter his Username, email address and full name.


3. After entering everything check it again and click on submit.
4. After succeful search for the user Facebook will show some information about how many emails are linked to the account and there is simple option saying 
No Longer Access to These click that one.
5. Now it will promote you to enter a new email address on which you will get the password resetting option so enter your email address I suggest you creating a Fake or Temporary email address for safety purpose.


6. Than it will promote you to enter the Security well if you have some security guess about that one than that’s ok but if you don’t know it than simply enter 3 wrong answers and it will take you to the 3 trusted friends recovery page like below.

7. Now just click continue and facebook will ask you to choose 3 trusted friends choose the 3 fake profiles of your which you created and added into the victims account. 
8. After selecting 3 accounts facebook will send security codes to these accounts just enter these codes and you will get Password Resetting email from Facebook on the account you created in Step 5

That’s it now you are successful in Hacking Facebook Password with the 3 Trusted Friends Method.

AnonPlus Hacked By SyRiAn Cyb3r Army


Boom Third Attack on AnonPlus.com  . Anonplus.com had been hacked once by AKINCILAR and then Th3 Pr0 & SaQeR SyRia now The SyRiAn Cyb3r Army Hacked it for the third time 


After the hacking gang Anonymous took credit for defacing Syria's Ministry of Defense website, a Syrian group retaliated on Monday by posting gruesome photos on Anonymous embryonic social network. 
The defacement of AnonPlus (http://anonplus.com/), the site Anonymous set up last month when it was booted off Google+ — did not include the name of the group responsible.


Where as Anonymous Claim that, AnonPlus is not their any Official site. Lulzsec leader Sabu tweeted "Turns out people were correct: anonplus.com was a troll domain. Belongs to "fro" aka "cnaperth" aka "Adam Bennett" from Perth, Aussie."


RefRef - DDOS Tool By The Anonymous

RefRef - DDOS Tool By The Anonymous

Previously you saw the source code of XerXes by The Jester . The Anonymous Team Have Also Developed their own DDoS tool which is said to exploit SQL vulnerabilities to support the group's future campaigns. Previously they had been using LOIC for many of their operation . But due to this tool many of the Anonymous got caught may the tool was not capable of hiding their tracks . So this time they made their own.


According to Developer "RefRef is a revolutionary DoS java site. Basically, by using an SQL and .js vulnerability, you can send a page request packet from your home computer with embedded .js file, because of the vulnerability in the SQL/Javascript engine on MOST websites, the site actually TEMPs the .js file on its own server. So now the .js is in place on the host of the site. Next since you still have the request, it picks up the .js file, and all of the requesting for packets power happens on the server, not the requestee. I send two packets from my iphone, and everything else happens on the server. Basically eats itself apart, because since both are on the server, its all a local connection."


This DDOS tool #RefRef s set to be released in September, according to an Anon promoting it on IRC this afternoon Developed with JavaScript, the tool is said to use the target site’s own processing power against itself. In the end, the server succumbs to resource exhaustion due to #RefRef’s usage. An attack vector that has existed for some time, resource exhaustion is often skipped over by attackers who favor the brute force of a DDoS attack sourced from bots or tools such as LOIC.


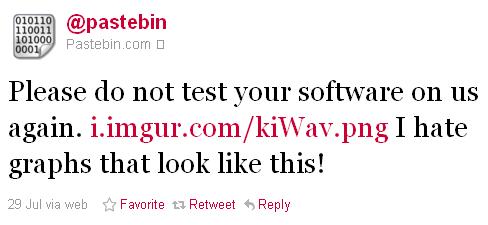
The tool is very effective, a 17-seconds attack from a single machine resulting in a 42-minute outage on Pastebin yesterday. The Pastebin Admins Weren't happy and tweeted 


The effectiveness of RefRef is due to the fact that it exploits a vulnerability in a widespread SQL service. The flaw is apparently known but not widely patched yet. The tool's creators don't expect their attacks to work on a high-profile target more than a couple of times before being blocked, but they don't believe organizations will rush to patch this flaw en masse before being hit.


This means there are a lot of possible targets out there that will be hit at least once. "This tool only makes you vulnerable if you don't keep your systems patched, perform the basic security, which is how Sony got caught with it's pants down," the RefRef developers said.


The tool works by turning the servers against themselves. It sends malformed SQL queries carrying the payload which in turn forces the servers to exhaust their own resources. However, the tool's GUI does have a field for inputting the refresh interval so it might combine traditional forms of HTTP hammering with the new technique.
Some security experts have been skeptical that the success of Anonymous's DDoS attacks can be explained through LOIC alone. They proposed that some of the group's supporters also have access to botnets, a theory that has partially proven to be correct.


source

SAP Systems on the Internet will be Hacked Next Week


On the 4th of august at the world’s largest technical security conference – BlackHat USA 2011, which will take place in Las Vegas, SAP security expert and CTO of ERPScan Alexander Polyakov will show how any malicious attacker can get access to the systems running on SAP via Internet using new critical vulnerability.
SAP systems are used in more than 100 000 world companies to handle business-critical data and processes. Almost in each company from Forbes 500 system data are set for the handling of any process beginning from purchasing, human resources and financial reporting and ending with communication with other business systems. Thus receiving an access by the malicious attacker leads to complete control over the financial flow of the company, which can be used for espionage, sabotage and fraudful actions against hacked company.
The given attack is possible due to dangerous vulnerability of the new type, detected by Alexander in J2EE engine of SAP NetWeaver software, which allows bypassing authorization checks. For example it is possible to create a user and assign him to the administrators group using two unauthorized requests to the system. It is also dangerous because that attack is possible on systems, protected by the two-factor authentication systems, in which it is needed to know secret key and password to get access. To prove it researchers from ERPScan created a program, which detects SAP servers in the Internet with help of secret Google keyword and checks found servers on potential dangerous vulnerability. As the result, more than half of available servers could be hacked with help of found vulnerability.

“Danger is in that it is not only a new vulnerability, but a whole class of vulnerabilities that was theoretically described earlier but not popular in practice. During our research we only detected several examples in standard system configuration, and because each company customizes the system under its own business processes, new examples of vulnerabilities of the given class can be potentially detected at each company in the future. We have developed a free program which can detect unique vulnerabilities of such type in order to protect companies on time and it is also included in our professional product – ERPScan Security Scanner for SAP.” — noted Alexander.
Source

Anonplus Hacked Again by Th3 Pr0 & SaQeR SyRia


Anonplus.com official social network was hacked by AKINCILAR some days before. 


Today i was going through the post when i saw a comment  saying 


anonymouse got hacked again, now from syrian hacker. :)
Hacked By The Pro & SaQeR SyRia :) 24/07/2011 at 13:04 GMT

anonymouse yol gecen hani olmus simdide, suriyeliler hacklemis...
Hacked By The Pro & SaQeR SyRia :) 24/07/2011 at 13:04 GMT


I went to http://www.anonplus.com/ and  it was defaced. 

Anonymous Got Hacked Another Time . First By AKINCILAR and now by Th3 Pr0 & SaQeR SyRia. 

Pakcyberarmy database Leaked by Indian Hacker

Indian Hacker - Lucky managed to crack  1500+ user passwords from Pakcyberarmy.net database. Pakcyberarmy.net is the hub of most of the Pakistani hackers. Indian hacker group "Indishell" leader "Lucky" leaks all info via a excel file available for download.
           DOWNLOAD THE PASSWORD LIST 
                               Archive password - proud_to_be_indian


I personally feel this cyber wars are just a medium to get fame nothing more.This silly attacks leaking personal information is encouraging the youth to do the same so that they can also get a name in this www society. But you should also understand that fame doesn't matter knowledge does.

Hackers Family Tree | Hacker Groups Relationships

Many People are still confused by all the hacking groups that were and ruling the internet now.You must be confused between the connection between Anonymous , LulzSec and AntiSec . Why Team Poison attacked  LulzSec and Anonymous. Ahh it is really confusing even i get confuse at times.

Geekosystem created a info-graphic chart describing his flowchart-like layout.Eric Limer writes, "Events are listed in unscaled but roughly chronological order from top to bottom." It's mostly helpful in seeing how the different groups are connected to each other and where they branch off on special projects. There's even some color coding and visual cues to show who's friends with whom and what those relationships begat in the recent history of hacking. There's not, however, much explanation about the projects or the groups. We've done our best to itemize and explain everything with a handy hacker glossary.


The Anonymous Branch


4chan - Started by Christopher Poole (screenname: moot) created this anonymous, image-based forum in his New York City bedroom at age 15. Since its launch in 2003, 4chan has grown to become one of the most trafficked forums on the internet with nearly seven million unique visitors a month. The culture at 4chan is both incredibly creative--memes like lolcats and Rickrolling started on 4chan boards--as well as potentially destructive--4chan users hacked Gawker and released the account info of all their users earlier last year.


Anonymous - The name of the Anonymous, leaderless hacking group originated on 4chan in 2003, and it's believed that various members of Anonymous met there. In 2008, an unofficial spokesperson Trent Peacock described the group on a Canadian Broadcasting Corporation radio show:


Anonymous
uses the Guy Fawkes mask from V Is for Vendetta as one logo and a headless businessman for others. Beyond iconography, however, the history of Anonymous is best told through a timeline of its projects.


Project Chanology -Project Chanology (also called Operation Chanology) is a protest movement against the practices of the Church of Scientology by members of Anonymous, a leaderless Internet-based group that defines itself as ubiquitous. The project was started in response to the Church of Scientology's attempts to remove material from a highly publicized interview with Scientologist Tom Cruise from the Internet in January 2008.Though that war took many forms--prank calls, black faxes, denial-of-service attacks--it all started with this YouTube video:


YouTube Porn Day - After the long fought battle with the Church of Scientology and a few other smaller projects, members of Anonymous teamed up with eBaum's World users to declare YouTube Porn Day on May 20, 2009. The protest itself, as the name sort of suggests, involved countless people uploading porn to YouTube to annoy the moderators who would then have to remove the videos. It took YouTubedays to remove all of the videos. The group repeated the action in 2010 "in protest of YouTube's decision to suspend the account of Lukeywes1234," an otherwise typical user whose account was suspended for abuse language:


Operation Payback - Anonymous did some work around the 2009 Iran election protests and Australian internet policy, but they gained global notoriety as a activists--or more appropriately, "hacktivists"--for their support for WikiLeaks. Although the project started in September 2010 as a war against the recording industry for opposing internet privacy, it evolved. Beginning in late November 2010, when the first U.S. diplomatic cables were released by WikiLeaks, Anonymous latched onto the cause and launched Project Avenge Assange, an attack on banks and credit card companies who froze WikiLeaks donations.


AnonOps.US - This subgroup of Anonymous spun off in mid-October 2010 when Operation Payback hit a lull. They bill themselves as an infrastructure for the group, and their internet relay chat (IRC) network remains acentral hub for activity amongst various hacker group. They also maintain a Twitter account with updates.


Operation Leakspin- Anonymous conceived of Leakspin in December 2010 as a way to help WikiLeaks sort through data. Unlike Operation Payback, which was bent on destruction, Leakspin focused on exposing information for the public good, and the effort still survives across a number of websites.
Attack on HB Gary - After Aaron Barr, chief executive of the internet security firm HBGary, announced that he would reveal the inner workings of Anonymous at a conference in February 2010, the group brought down their website and phones, erased files and pulled over 68,000 emails from their database. Within those documents was a PowerPoint presentation called "The WikiLeaks Threat" which HBGary compiled for Bank of America in order identify and potentially disrupt the activities of journalists who supported the movement, including Glenn Greenwald.
Operation Sony -  Sony filed a lawsuit against George Hotza hacker who reverse engineered the Sony Playstation 3, in January 2011. In response, Anonymous announced that they would attack Sony's website in early April 2011. Three weeks later, the entire Playstation network was brought down, and Sony was unable to restore the network for weeks. Anonymous cheekily denied responsibility for the attack, although Sony reports having discovered a document named "Anonymous" on their servers that read "We Are Legion." . 
Operation Orlando - Anonymous attacked the websites of the Orlando Chamber of Commerce and Universal Orlando Resort in June 2011 after police there arrested Food Not Bombs volunteers for breaking city ordinances while trying to feed the homeless. HackerLeaks, a WikiLeaks-type site just for hackers, was created as a result.
The LulzSec Branch 
LulzSec Lulz Security, commonly abbreviated as LulzSec, was a computer hacker group that claimed responsibility for several high profile attacks, including the compromise of user accounts from Sony Pictures in 2011. The group also claimed responsibility for taking the CIA website offline. The group has been described as a "cyber terrorism group" by the Arizona Department of Public Safety after their systems were compromised and information leaked. It has gained attention due to its high profile targets and the sarcastic messages it has posted in the aftermath of its attacks.
AntiSec - LulzSec disbanded in June 2011 but not before they announced a new project that reunited LulzSec members with the leaders of Anonymous. This hacktivism project began with a major release of documents from law enforcement officers in Arizona.

The Web NinjasTeaMp0isoNThe A-Team and th3j35st3r -

TeaMp0isoN TeaMp0isoN is a British hacker group. According to the group member TriCk (also known asSaywhat?), the core of the group consists of three members who know each other online for five years but never met in person.Another member of the group uses online nick iN^SaNe .

The Jester (also known by the leetspeak handle th3j35t3r) is a self-described gray hat "hacktivist" who is allegedly responsible for attacks on WikiLeaks, 4chan, Iranian President , Mahmoud Ahmadinejad, and Islamist websites.He claims to be acting out of American patriotism.The Jester developed and uses the denial-of-service (DoS) tool known as "XerXeS". One of The Jester's habits is to tweet "TANGO DOWN" on Twitter whenever he successfully takes down a website.

Source :- 

Wikipedia 

Facebook Hires Sony's PS3 Hacker ‎

Facebook Hires Sony's PS3 Hacker ‎

Facebook hires Sony hacker
June 29 2011

New York - The 21-year-old computer whiz whose legal tussle with Sony triggered one of the largest assaults by the hacker community on a single company has found himself a steady job - with Facebook. George Hotz became a star among hackers under the internet pseudonym name GeoHot when he “unlocked” Apple's iPhone and then the Sony PlayStation games console. He posted details of how to alter software on the devices so that tech-savvy users could use them for unauthorised games and other applications.

Facebook swooped to hire Mr Hotz last month, just weeks after he settled the lawsuit from Sony that so enraged fellow hackers that they launched an attack on the company that has cost it tens of millions of dollars to date.

The social networking giant has not said what Mr Hotz will be working on, though there was speculation he could be involved in building anti-hacker defences at Facebook, or in the company's plans to develop a rival to Apple's App Store for software downloads.

Mr Hotz is straight out of hacker central casting, a teenage computer genius who grew up in New Jersey and was identified early as a talented youngster, attending a special programme for bright children from the US state school system. He led his school in national robot-building championships and appeared on national television demonstrating his creations.

It was in 2008 that he achieved fame in the hacker community for conducting the first so-called “jailbreak” of an Apple iPhone. His hack allowed users to get round Apple's tight controls on what apps can be downloaded to the phone and which mobile phone networks it can be used on.

And then in 2009 and 2010, he chronicled on his blog his attempts to similarly unlock Sony's PlayStation 3 console, and earlier this year he posted “root keys” for the PS3 so that others could emulate his work and build homegrown software on the device. Sony launched a lawsuit days later, saying Mr Hotz was encouraging the use of pirated games.

In an interview on the cable TV channel G4, Mr Hotz put himself in the tradition of radio hams of old and said he was fighting for the right for computer fans to tinker with their equipment. “This is about a lot more than what I did and me,” he said of the lawsuit. “It's about whether you really own that device that you purchase.”

Facebook's decision to hire Mr Hotz sends a powerful signal that it will be a welcoming employer for the brightest engineers. Google bosses last year said they were in a “war for talent” with Facebook and other Silicon Valley firms, and the war is only likely to hot up now that money is flowing into the technology industry from investors keen to find the next Facebook.

As Mr Hotz was yesterday ensconced in his new role, the fallout from his actions continued to reverberate. Sir Howard Stringer, the British businessman who runs Sony, faced calls for his resignation at the Japanese firm's annual shareholder meeting.

The company was forced to temporarily shut down its PlayStation Network of online games after disclosing in April that hackers had accessed personal information on 77 million of its customers, potentially including their credit card details.

Sir Howard said on Tuesday that the company had been the victim of a revenge attack by supporters of Mr Hotz. “We believe that we first became the subject of attack because we tried to protect our intellectual property, our content, in this case videogames,” he said. - The Independent
Share to Facebook Share to Twitter Stumble It More...
Related Posts Plugin for WordPress, Blogger...
 

Like Us !!

Story Box